Cyber Security Services Perth — SMB1001 Gold Certified

Managed Cyber Security Services Perth

Qbit's managed cyber security services protect more than 300 Western Australian businesses from threats that target sensitive data, disrupt operations and put regulatory compliance at risk. We are ISO 27001 certified and SMB1001 Gold certified, and every Qbit Managed Security Services agreement puts your business at the SMB1001 Silver standard as part of the monthly service.
managed cyber security services

Why Managed Cyber Security Services Matter

Most small and medium businesses can’t justify a full-time security team, but they face the same threats as the organisations that can. A single breach means lost revenue, a damaged reputation and, increasingly, a compliance problem with clients and insurers asking what controls you had in place. 

Managed cyber security closes that gap. You get enterprise-grade protection, continuous monitoring and specialists who respond when something happens, for a predictable monthly cost, without hiring anyone. 

It also works alongside an internal IT team. Our Managed Security Services agreement can be taken on its own, without moving your IT support to Qbit. Your IT manager keeps running the systems they know best, while responsibility for security monitoring, threat response, patching oversight and compliance evidence sits with us, backed by our ISO 27001 certification and SMB1001 Gold status. For many internal IT managers, that is the difference between security being one more thing on the list and security being handled. 


300+ WA Business Protected, 95% of tickets closed in under 12 business hours, calls answered by one of our technicians on average in under 15 seconds

300+ WA BUSINESSES PROTECTED

More than 300 Western Australian businesses rely on Qbit to keep their systems secure and running. We support mining and exploration companies with remote sites, accounting and legal practices holding sensitive client data, medical practices, not-for-profits and WA Government agencies under CUAICTS2021.

Every one of those environments is monitored, patched and backed up under a managed agreement, with 24/7 detection and response behind it. Our ISO 9001 quality objective is to answer your call within 30 seconds — in practice we average under 15. And 95% of tickets close within 12 business hours.

We are ISO 27001 certified for information security and hold SMB1001 Gold, both independently audited. The controls we put in your environment are the ones we run in our own.

managed wiring for cyber security

Our Cyber Security Risk Management Process & Approach

At Qbit, security isn’t an afterthought bolted onto IT support. It’s built into how we run our own business and how we run yours.

We are certified to ISO 27001 for information security and ISO 9001 for quality management, and we hold SMB1001 Gold. Those certifications are audited independently, so the standards we apply to your environment are the ones we are held to ourselves.

We work to a certifiable standard, not just a framework

SMB1001 is the Australian cyber security standard written for small and medium businesses. Unlike a framework, it is certifiable across graded levels, so your security posture becomes something you can prove to a client, an insurer or a tender panel rather than something you describe.

A Qbit Managed Security Services agreement, taken as presented, puts your business at the SMB1001 Silver standard. Higher levels are available where a contract or insurer requires them.

Where your organisation has other obligations, we can also align your environment to the Essential Eight or ISO 27001 — common requirements for government suppliers, defence contractors and larger enterprise clients.

This gives your business a structured path to compliance, stronger cyber resilience and protection against emerging threats, while your internal team stays focused elsewhere and we handle threat detection, vulnerability management and continuous monitoring.

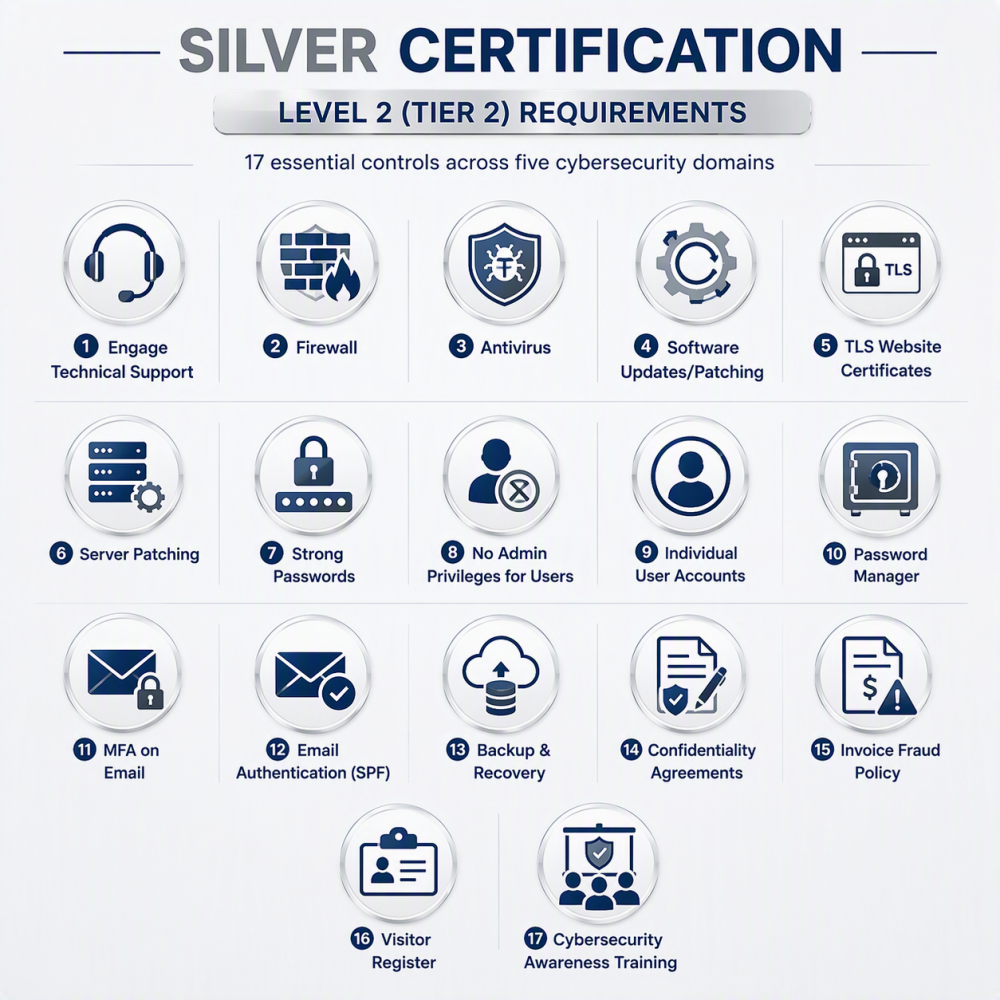
SMB1001 all 17 silver requirements

SMB1001 Certification, Built Into the Agreement

A Qbit Managed Security Services agreement, taken as presented, puts your business at the SMB1001 Silver standard. The controls are part of the monthly service rather than a separate security project you have to fund and run.

Qbit holds SMB1001 Gold in our own business, so the controls we implement for you are the ones we already run ourselves. Higher levels are available where a contract, insurer or tender panel requires them.

What the agreement covers:

  • Identity and access management: Multi-factor authentication, privileged access management and least privilege access help ensure users only have access to the systems and information required for their roles.
  • Endpoint and threat protection: Endpoint protection, application control, XDR and 24/7 MDR help detect, investigate and respond to suspicious activity across your IT environment.
  • Vulnerability and patch management: Regular assessments, software updates and remediation planning help identify and address security weaknesses.
  • Email and cloud security: Advanced email filtering and SaaS monitoring help protect Microsoft 365 and other cloud applications from phishing, compromised accounts and unauthorised activity.
  • Backup and recovery: Managed backups, recovery planning and testing help protect critical business information and support continuity following a cyber incident.
  • Security governance: Risk assessments, security policies, reporting and quarterly IT Management Plans provide evidence of ongoing security management and continuous improvement.
  • Security awareness: Staff training and phishing simulations can help address human risk and build a stronger security culture.

Certification as a Service

Meeting the standard and holding the certificate are two different things. Certification is awarded independently, not by Qbit.

That’s what Certification as a Service is for. Included under your Managed Security Services agreement, it takes your business through independent SMB1001 certification and keeps you certified year to year — the assessment, the documentation, the evidence and the renewals.

Where your current environment has gaps to close first, we assess your position, give you a practical remediation plan, and quote that work up front so you know the full cost before you commit.

What’s Included in Our Managed Cyber Security Services

Our comprehensive cyber security services address every aspect of IT security to ensure robust protection for your business. Recognising that each business has unique requirements, we conduct an individual risk assessment to tailor solutions to your specific needs. Key risk management strategies can include:

Endpoint Detection & Protection

Advanced antivirus, anti-malware solutions, and endpoint detection solutions for all devices, from desktops, laptops, servers, and mobile phones.

XDR (Extended Detection & Response)

XDR is a technology-driven cyber security solution that unifies threat detection, investigation, and response across multiple layers: endpoints, networks, cloud workloads, email, and identities.

MDR (Managed Detection & Response)

Managed detection and managed security service is where a third-party provider delivers 24/7 monitoring, threat hunting, and rapid response using both technology and human expertise.

Email Security

Protect against phishing attacks, spam, and malware with advanced filtering and security tools for your email systems.

Firewall & Network Security

Enterprise-grade firewalls and intrusion detection systems to safeguard your security infrastructure and network perimeter.

SaaS Alerts

Monitor and manage activity across your cloud-based applications to detect security issues, prevent data breaches, and make sure that security requirements are met.

Privileged Access Management

Control and monitor access to critical systems, reducing the risk of insider threats and security vulnerabilities.

Application Control

Restrict and manage the applications that can run within your environment to reduce attack surfaces and prevent security incidents.

Data Backup & Disaster Recovery

Regular backups and tested recovery plans to maintain business continuity, even in worst-case scenarios like natural disasters or system failures.

Policy & Compliance Management

Assistance with implementing security programs, security policies, and meeting industry compliance standards.

Quarterly IT Management Plans

Prepared by your dedicated account manager, these plans deliver actionable insights and strategic recommendations to strengthen your IT infrastructure and enhance your cyber security posture.

Security Risk Assessments

Annual audits to identify vulnerabilities and strengthen your cyber security posture.

Why Do Australian Businesses Choose Qbit for Managed Cyber Security Services?

Qbit is ISO 27001 certified.
Established in 2006, now trusted by over 300 Western Australian businesses.
Our ISO 9001 quality objective is to answer your call within 30 seconds - in practice we average under 15.
Predictable costs with fixed monthly pricing for complete peace of mind.
qbit team

Partner With Perth’s Trusted Managed Security Service Providers

Don’t wait for a security incident to disrupt your core operations. Contact Qbit today for a Free Security Assessment and discover how our managed security services can protect your organisation’s digital assets from evolving cyber security risks.

Frequently Asked Questions

According to the ACSC’s Annual Cyber Threat Report for 2024 to 2025, the top cyber risks are:

  • Credential theft or compromised accounts
  • Phishing
  • Ransomware
  • Identity fraud and scams
  • Supply chain attacks

Our managed cybersecurity services are offered on a flexible, per-user, per-month pricing model. You can customise your solution by adding security products, Advanced Microsoft 365 security tools, and other cybersecurity services to meet your business’s specific security requirements.

MDR (Managed Detection & Response) focuses on 24/7 threat detection, incident management, and rapid response from security experts. On the other hand, MSS (Managed Security Services) provides a wider range of security services. This includes monitoring, management of intrusion detection systems, antivirus software, and overall security posture maintenance. 

Extended Detection and Response, or XDR, is a cybersecurity technology that collects and analyses security information across endpoints, email, identities, servers, networks and cloud applications. Rather than examining each system separately, XDR connects activity across the environment to identify patterns that may indicate a cyberattack. This gives security specialists greater visibility and helps them investigate, contain and respond to threats faster.

Antivirus is primarily designed to identify and block malicious files or software on an individual device. Managed Detection and Response, or MDR, provides a broader managed security service that combines advanced detection technology with human cybersecurity expertise. MDR specialists monitor your environment 24/7, investigate suspicious activity and respond to confirmed threats. Antivirus remains an important layer of protection, but MDR provides the continuous monitoring and active response businesses need to defend against more sophisticated attacks.

Privileged Access Management, or PAM, protects accounts with elevated permissions, such as administrator accounts that can change system settings, access sensitive information or manage other users. PAM can control who receives privileged access, require additional authentication, securely manage administrator credentials and record privileged activity. This reduces the risk of powerful accounts being misused by attackers, employees or unauthorised third parties.

Least privilege access means giving each user, application or system only the minimum level of access required to perform its authorised function. For example, an employee who does not need to install software should not have local administrator permissions. Applying least privilege access helps reduce accidental changes, unauthorised access and the ability of an attacker to move through the business network after compromising an account. Access should also be regularly reviewed and removed when roles or employment circumstances change.

Yes. The Managed Security Services agreement is available on its own, alongside your internal IT team or your existing support provider. Managed IT Services always includes the security agreement, but the security agreement can stand alone.

Get Expert Insights with a Free IT Assessment

Want to know what your IT could look like? Book a free 30-minute assessment.